Your cloud. Graphed, pentest-proven, audit-immutable.
Arkhein unifies AWS, Azure, GCP, OCI and Huawei Cloud into a living graph — combining active attack-path emulation, closed-loop remediation (NL → PR), and compliance dossiers with cryptographic custody.
One sovereign platform · Five clouds · Continuous audit-ready attestation


One graph. Every cloud. Real answers.
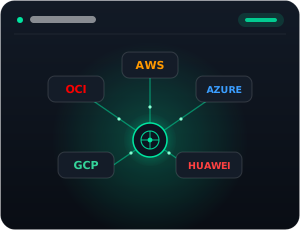
Clouds unified on one graph — AWS · Azure · GCP · OCI · Huawei
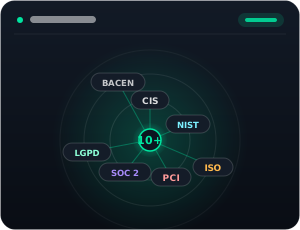
Compliance frameworks mapped — BACEN 4893, LGPD, PCI-DSS, SOC 2, ISO 27001
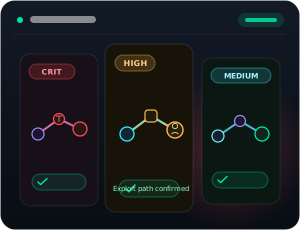
Of findings prioritized by real architectural choke points
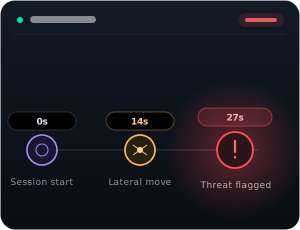
Ghost Mode flags and halts lateral movement in under 30 seconds
Continuous Regulatory Proof, Cryptographically Sealed.
From global finance and enterprise SaaS to healthcare and national sovereignty: Arkhein connects regulatory mandates to the real state of your multi-cloud infrastructure — transforming ephemeral telemetry into continuous, mathematically verifiable proof.
Global Standards are the requirement
PCI-DSS 4.0, BACEN 4.893 & IN 85, DORA, SOC 2, ISO 27001, HIPAA, and LGPD/GDPR demand continuous control verification, zero-trust segmentation, and immutable audit trails.
Arkhein is the control layer
Living graph correlation across AWS, Azure, GCP, OCI, and Huawei. Continuous attack path detection, choke point mitigation, and closed-loop GitOps remediation via Terraform PRs.
Master Attestation Vault is the proof
Evidence is part of the product, not post-audit paperwork. Cryptographically signed dossiers (ECDSA P-256) verifiable by external auditors without platform credentials.
PCI-DSS 4.0, BACEN & DORA
Continuous verification of PCI-DSS 4.0 (Req. 11.4 continuous pentest), BACEN Resolução 4.893 / IN 85 (Articles 8, 9, 10, 11), and EU DORA (Articles 9, 10, 12, 26). Automated correlation ensures banking systems remain resilient and audit-ready around the clock.
SOC 2 Type II & ISO 27001:2022
Full-spectrum mapping against SOC 2 Trust Services Criteria (CC6.1, CC6.6, CC6.7, CC7.2) and ISO/IEC 27001:2022 Annex A controls (A.5.15, A.8.3, A.8.20, A.8.24). Zero-friction B2B security reviews backed by continuous posture verification.
HIPAA, LGPD & GDPR Sovereign Vault
Strict ePHI protection under HIPAA Security Rule (§164.312), GDPR (Articles 25, 32), and LGPD (Article 46) combined with Brazilian Banking Secrecy (LC 105). Sovereign on-prem and VPC deployment guarantees zero data egress and complete data isolation.
Cryptographic Proof & /verify
Every compliance report and evidence bundle is sealed with ECDSA P-256 digital signatures and SHA-256 hashes. External regulators (BACEN auditors, PCI QSAs, Big Four) verify authenticity instantly on the public verification portal without platform logins.
Everything an attacker sees —
before they do.
One graph, from discovery to remediation — not another list of findings.
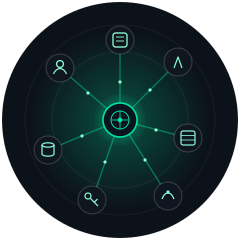
Security Graph
Every resource, identity, and relationship across your clouds in one queryable graph — enriched in real time by event streams and out-of-band workload telemetry.
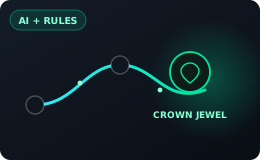
Attack Path Analysis
Ghost Mode runs deterministic + AI attack-path analysis to surface the real, exploitable routes to your crown jewels.
CSPM, DSPM & Compliance
Continuous posture and deep sampling DSPM across S3 and OBS buckets, mapped to CIS, NIST, ISO, PCI, SOC 2, LGPD and BACEN — with exportable audit proof.
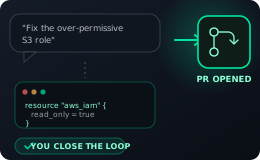
Closed-Loop Remediation & Containment
From graph choke points to automated runtime containment or synthesised Terraform PRs with Checkov AST validation. Findings close atomically upon merge.
From cloud accounts to closed findings.
Four steps, one loop — no agents, no friction.
1
Connect
Onboard AWS, OCI, GCP, Azure and Huawei Cloud in minutes with scoped, read-only roles.
2
Scan
Prowler and the Go scanner map every resource, identity and misconfiguration.
3
Analyze
Arkhein builds the graph, scores risk and finds cross-cloud attack paths.
4
Remediate
Ship fixes as Terraform pull requests and export compliance evidence.
Pricing that scales with
your cloud footprint.
Annual contracts, billed once a year. No self-serve monthly plan — every engagement starts with a demo sized to your environment.
Professional
For teams getting started on cloud security
$
≈ $9,167/mo · billed annually
- Up to 5 cloud accounts (AWS, GCP, Azure, OCI or Huawei Cloud)
- Up to 500 IPs and 30 K8s nodes
- Security Graph + CSPM + CIS Benchmarks (5 providers)
- Ghost Mode v2 — 20 reports/month
- SIEM + CDR + UEBA (4 providers)
- CIEM + Container Security + IaC Scanning
- Regulatory Engine — 3 frameworks
- Ask Arkhein — 200 queries/month
Scale
For scaling cloud security programs
$
≈ $14,583/mo · billed annually
- Up to 15 cloud accounts (AWS, GCP, Azure, OCI, Huawei Cloud)
- Up to 1,000 IPs and 75 K8s nodes
- Everything in Professional
- Ghost Mode v2 — Unlimited
- Puppet Master APE — 12 engagements/year
- AI Intelligence Layer + RESPOND (HITL)
- Regulatory Engine — 5 frameworks
- Container Security (EKS / OKE / GKE)
- Priority support
Enterprise
For large enterprises — self-hosted option available
Custom
Custom contract · self-hosted option available
- Everything in Scale, plus:
- Unlimited cloud accounts (AWS, GCP, Azure, OCI, Huawei Cloud), self-hosted option
- Unlimited Puppet Master engagements
- AI Management Agent + RESPOND autonomous
- SSO/SAML, SLA 99.9%, Professional Services
Answers for security and
compliance teams
Clear answers about how Arkhein secures your multi-cloud — from onboarding to business move forward.
Arkhein connects your AWS, OCI, GCP, Azure and Huawei Cloud accounts and builds a living graph of every resource, identity and relationship. It runs continuous CSPM scans, finds cross-cloud attack paths with Ghost Mode, maps compliance, and can ship fixes as Terraform pull requests.
Scanners hand you thousands of isolated findings. Arkhein connects them on a graph, so you see the real path an attacker would take to your crown jewels — and fix the choke point instead of the checklist. It is also available self-hosted, which SaaS-only vendors don't offer.
AWS, OCI, GCP, Azure and Huawei Cloud today. Compliance is mapped to CIS, NIST 800-53, ISO 27001, PCI-DSS, SOC 2, LGPD and BACEN, with exportable evidence for auditors.
Connecting an account takes minutes with scoped, read-only roles — no agents. Your first attack-path analysis is ready within the first scan, and guided onboarding is included.
Yes. Credentials are encrypted, access is scoped and read-only, and every action is audited. For regulated or data-sovereign environments, Arkhein can run fully self-hosted in your own infrastructure.
Arkhein is priced by value and cloud footprint, in three tiers from Professional to Enterprise. There is no self-serve trial — book a demo and our team will size the right plan for your environment.
We'd love to hear from you.
Whether you're ready to start a project or have questions, our team is here to help.
Ready to see your cloud
as an attacker does?
Book a demo and our team will walk you through Arkhein on your own cloud.